Empowering Your Business to Stay Ahead in Compliance and Regulations
You can Focus on Growth with Our IT Consulting
NCA (National Cyber Security Authority)
GRC 360 consulting services adhere to the highest standards of quality, security, and continuous improvement, ensuring your journey to IT excellence is backed by certified expertise and commitment. By integrating artificial intelligence into cybersecurity, we deliver advanced, proactive protection that keeps your organization secure and resilient.
The National Cybersecurity Authority (NCA) of Saudi Arabia developed the Essential Cybersecurity Controls to conduct a comprehensive study of multiple national and international cybersecurity frameworks and standards. This involved studying related federal decisions, laws, and regulatory requirements, as well as reviewing and leveraging cybersecurity best practices.
CST (Communication Space and Technology)
Communication, space, and technology are interconnected realms continually shaping and revolutionizing human interaction and progress. The convergence of these domains has propelled innovation, enabled global connectivity and expanded our understanding of the universe. Advancements in space technology have facilitated communication on Earth and fostered new communication methods beyond our planet. Satellite technology, for instance, has revolutionized telecommunications, allowing for instantaneous transmission of data, voice, and images across vast distances.
SAMA (Saudi Arabian Monetary Authority)
The Saudi Arabian Monetary Authority (SAMA) has undertaken the responsibility to improve Cyber Resilience by adopting the industry’s best practices, Standards, and other Frameworks and thus formulating the SAMA Cyber Security Framework. The authority employs advanced technologies and collaborates with domestic and international cybersecurity experts to continually enhance its defenses. As technology continues to advance, SAMA remains committed to staying at the forefront of cybersecurity efforts to mitigate risks and uphold the resilience of Saudi Arabia’s financial infrastructure.
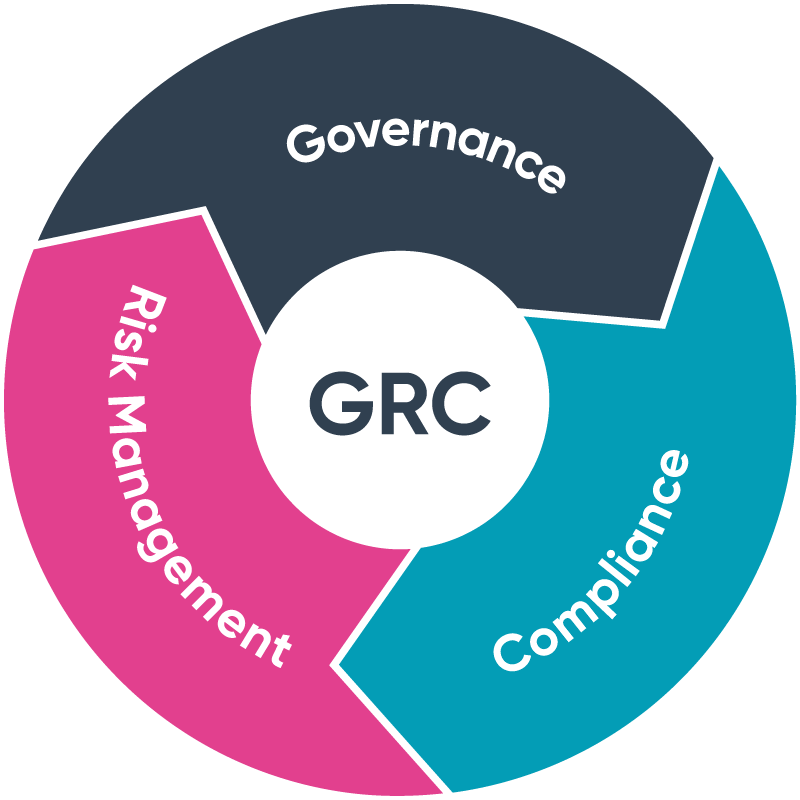
Empowering Your Business
GRC-360's Strategic Approach to Governance, Risk, and Compliance Challenges
While GRC offers a structured framework for managing complex issues, there are challenges organizations face, such as:
- Evolving Regulatory Landscape: Businesses face compliance risks and possible legal repercussions when navigating the complex web of ever-changing legislation.
- Cybersecurity Risks: Businesses are facing an increasing number of cyber attacks, which might result in anything from data breaches to major disruptions to operations.
- Operational Inefficiencies: Ineffective governance frameworks and procedures can impede operations, resulting in mistakes, delays, and higher expenses.
- Reputation Management: A compliance failure or security breach can tarnish a business’s reputation, eroding stakeholder trust.
The Discovery Phase is Important
Spending time taking stock of existing processes is vital if the GRC program is to be a success.
Onboarding Senior Management
The benefits of a unified GRC approach should be clear to any members of senior management.
GRC Tools Can Streamline the Process
GRC tools, such as reliable board portal software, will help streamline the project.
Define Objectives and Keep Communication Channels Open
Circling back to the goals of your GRC initiative is critical.
Two Approaches to Compliance Management
A compliance management solution can vary from simple to complex and must be uniquely tailored to suit an organization’s structure and industry. Two common methods of compliance management are:
Strict, Top-Down Approach
This is the most rigid approach to compliance management. Internal policies are created and implemented by the person or team at the top of the organizational chart.
Hands-Off Approach
In contrast, a hands-off approach is the most flexible type of compliance management.